

WorkOS Audit Logs
WorkOS Audit Logs record the security-relevant actions taken in your application and organizations — capturing the actor, action, target, timestamp, and contextual metadata for each event. RunReveal ingests them from a WorkOS Audit Log stream so you can retain, search, and build detections on administrative and end-user activity.
Ingest Methods
RunReveal offers the following ways to ingest WorkOS Audit Logs:
- Webhook — WorkOS streams events to a RunReveal webhook URL via a Generic HTTPS log stream
- AWS S3 Bucket
- Google Cloud Storage
The webhook method imports events with the lowest latency. Object storage can be cheaper at high volume but adds some delay.
If you use an AWS S3 bucket, send bucket notifications to the SNS topic for the RunReveal app you sign in to.
app.runreveal.com
Replace <REGION> with the AWS region where your S3 bucket is located (e.g., us-east-1, us-west-2, eu-west-1).
SNS topic & Custom SQS. Use the ARN above in your event notification tied to your S3 bucket—the topic name must match (runreveal_…; hyphens in the source id become underscores). For Custom SQS, set the queue URL and region in RunReveal; see AWS S3 Bucket with Custom SQS.
Note: BYOC, On-Prem, and BYODB customers must use their AWS account ID in the ARN instead of 253602268883.
Setup
Create the RunReveal Source
- Go to Sources in RunReveal
- Click the WorkOS Audit Logs source tile
- Give it a name and select the Webhook ingest method
- Click Connect Source
- Copy the Webhook URL. No bearer token is generated for this source, and none is required.
Create the WorkOS Audit Log Stream
- Sign in to the WorkOS Dashboard
- Navigate to Audit Logs and open Log Streams (or Streaming)
- Create a new log stream and choose the Generic HTTPS destination
- Set URL to the RunReveal Webhook URL you copied (
https://api.runreveal.com/sources/workos-audit/webhook/<id>) - WorkOS requires HTTP Header Name and HTTP Header Value, but RunReveal does not check them. Enter any placeholder, for example
X-Sourceandrunreveal. Use a custom header name rather thanAuthorization. - Set Request Body Format to Standard JSON. Newline delimited JSON (NDJSON) is also supported.
- Save the log stream
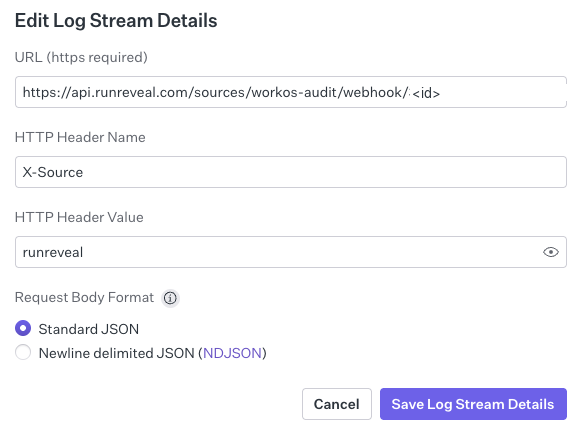
RunReveal does not validate the header WorkOS sends, and there is no bearer token or HMAC signature to configure. The webhook URL is the only value this source needs.
Emit Audit Log Events
Audit Log events are emitted by your application through WorkOS (via the Audit Logs API or WorkOS-managed actions). Once the stream is active and events are being emitted, they will begin flowing to RunReveal.
Regardless of ingest method, events are stored under the single workos-audit source type, so your queries and detections work the same whether you use the webhook or object storage.
Verify It's Working
Once configured, logs should begin flowing as audit events are emitted.
You can validate we are receiving your logs by running the following SQL query.
Schema
The following columns are exposed for this source. RunReveal applies schema normalization across all sources, ensuring uniform field names and data types for cross-source queries and reusable detection logic.
Table: workos_audit_logs (49 columns)
workos_audit_logs (49 columns)| Column | Type |
|---|---|
workspaceID | String |
sourceID | String |
sourceType | String |
sourceTTL | UInt32 |
receivedAt | DateTime |
id | String |
eventTime | DateTime |
eventName | String |
eventID | String |
srcIP | String |
srcASCountryCode | String |
srcASNumber | UInt32 |
srcASOrganization | String |
srcCity | String |
srcConnectionType | String |
srcISP | String |
srcLatitude | Float64 |
srcLongitude | Float64 |
srcUserType | String |
dstIP | String |
dstASCountryCode | String |
dstASNumber | UInt32 |
dstASOrganization | String |
dstCity | String |
dstConnectionType | String |
| Column | Type |
|---|---|
dstISP | String |
dstLatitude | Float64 |
dstLongitude | Float64 |
dstUserType | String |
actor | Map(String, String) |
tags | Map(String, String) |
resources | Array(String) |
serviceName | String |
enrichments | Array(Tuple(data Map(String, String), name String, provider String, type String, value String)) |
readOnly | Bool |
rawLog | String |
action | String |
eventVersion | UInt32 |
actorID | String |
actorName | String |
actorType | String |
location | String |
userAgent | String |
organizationID | String |
targetType | String |
targetID | String |
targetName | String |
targets | String |
metadata | String |
Helpful Links
- WorkOS Audit Logs - Product overview and concepts
- WorkOS Audit Log Streams - Configure Generic HTTPS and S3 log stream destinations
- WorkOS Dashboard - Manage Audit Logs configuration